
A modern smartphone might contain banking apps, private conversations, work documents, passwords, photos, health information, and dozens of third-party applications from developers you have never met.
Letting all of those apps freely interact with one another would be a security disaster. That is why modern mobile platforms do not rely on a single barrier to keep applications separated.
Instead, they combine several mechanisms such as process isolation, application sandboxes, file permissions, runtime permissions, mandatory access controls, code signing, secure inter-process communication, and hardware-backed security.
Understanding why mobile operating systems use multiple layers of app isolation helps explain how smartphones can safely run hundreds of applications on the same device.
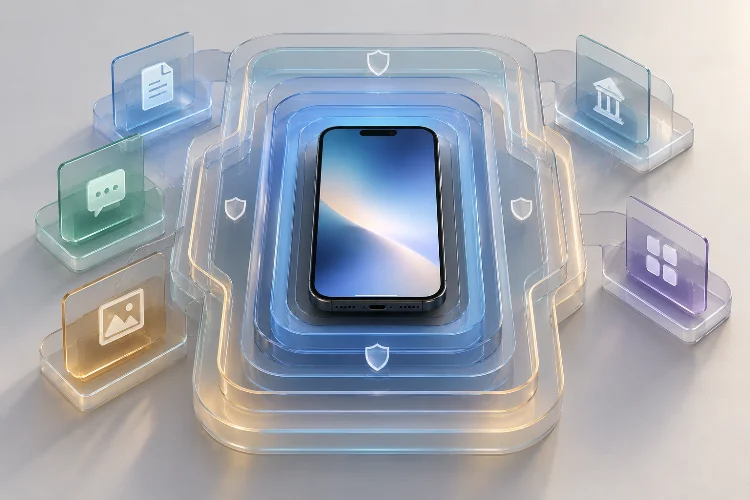
The basic idea is known as defense in depth. No individual protection is assumed to be perfect. If one boundary fails, another layer should still make it difficult for a compromised app to reach sensitive data or take control of the system.
This layered approach turns app isolation from a simple wall into a series of locked doors.
App Sandboxing Creates the First Major Boundary
The application sandbox is one of the most familiar layers of mobile isolation.
Every app receives a restricted environment where it can store files and execute code without automatically gaining access to another application’s private data.
On Android, application isolation is built partly on Linux user identities. Apps normally receive unique user IDs, allowing the operating system to separate their files and processes.
Apple uses a comparable principle on iOS and iPadOS. Apple states that all third-party apps are sandboxed, with each application receiving its own unique home directory.
Apps that need information outside their container must access it through services explicitly provided by the operating system.
This is the first important security rule: an application should not automatically be able to see everything just because it is installed on the device.
Without that boundary, one malicious game could potentially browse through data belonging to banking, messaging, or password-management apps.
Process Isolation Protects Runtime Memory
File separation is only one part of the problem.
Applications also handle sensitive information while they are running.
A banking app might temporarily hold account details in memory. A messaging application may process decrypted conversations. A password manager may briefly handle credentials before filling them into another service.
Process isolation prevents unrelated applications from freely inspecting one another’s memory.
Android normally places apps into separate processes, supported by the underlying Linux security model. iOS similarly prevents ordinary third-party applications from arbitrarily reading the runtime memory of other apps.
This means compromising one application does not automatically mean compromising every running process.
An attacker who exploits a bug inside a photo editor, for example, may gain control over that app’s process. But reaching another application’s memory requires breaking through additional operating-system protections.
That extra difficulty is exactly what layered isolation is designed to create.
Permissions Open the Sandbox Only When Necessary
A completely isolated app would not be very useful.
Maps need location information. Video-chat software needs a camera and microphone. Photo editors may need access to images.
Mobile operating systems therefore use permission systems to create controlled openings in the sandbox.
Instead of automatically giving applications access to sensitive resources, the platform decides which capabilities require explicit permission.
Users may be asked whether an app can access location, contacts, photos, Bluetooth devices, the microphone, or the camera.
The important point is that these permissions sit on top of sandboxing.
An app begins from a relatively restricted position and gains specific capabilities only when allowed.
This follows the principle of least privilege: software should receive only the access it actually needs.
A weather widget might reasonably need approximate location information. It probably does not need unrestricted access to your microphone, messages, and entire photo library.
Keeping those privileges seperate reduces the damage a malicious or compromised app can cause.
Mandatory Access Controls Add Another Layer
Traditional file permissions are useful, but modern mobile systems need stronger controls.
Android uses SELinux, or Security-Enhanced Linux, as an additional enforcement layer.
SELinux uses mandatory access-control policies to define which processes can interact with specific system resources. These rules can restrict behavior even when a process has privileges that might otherwise allow broader access.
This is important because security cannot depend entirely on the application behaving properly.
Suppose an attacker compromises a process and attempts to perform an operation that normal app code should never need.
SELinux policies may block that action independently of the app’s own logic.
Android has gradually strengthened per-app SELinux isolation across platform releases, adding another boundary beyond the basic Linux application sandbox.
This gives Android multiple opportunities to stop an attack.
An attacker may need to escape the app process, bypass operating-system permissions, defeat SELinux policy, and then overcome additional protections before reaching high-value system resources.
Apple Uses Entitlements to Restrict Special Capabilities
Apple uses another mechanism called entitlements.
An entitlement grants a specific capability to an application, such as access to certain platform features or protected services.
Apple’s developer documentation describes entitlements as security permissions used to enable particular capabilities. Many sensitive capabilities are disabled unless an application has the appropriate entitlement.
This is different from simply asking the user for permission.
Some privileges must also be authorized as part of the application’s signed configuration.
That allows the platform to control not only what the user approves, but also what capabilities the application was designed and authorized to use.
Apple describes sandboxing as a way to contain damage to system resources and user data if an application becomes compromised.
The result is another layer between ordinary app code and sensitive operating-system functionality.
Controlled IPC Lets Apps Communicate Safely
Apps sometimes need to talk to each other.
A user might share a photo from one application to another, use a password manager to fill credentials, or open a payment flow that moves temporarily between apps.
Mobile systems cannot simply prohibit all communication.
Instead, they provide controlled inter-process communication, or IPC.
The idea is similar to using a reception desk instead of allowing visitors to wander freely through an office building.
An application sends information through a defined operating-system mechanism. The platform can enforce identities, permissions, data formats, and access rules during that exchange.
On Android, Binder provides a major IPC mechanism for communication between processes.
Apple provides controlled services and extensions that let apps share specific capabilities without giving them unrestricted access to each other’s private containers.
Well-designed IPC preserves isolation while still allowing mobile apps to cooperate.
The risk appears when developers expose too much functionality through these interfaces.
That is why secure platform architecture and secure app development must work together.
Code Signing Helps Establish App Identity
Isolation rules are easier to enforce when the operating system knows which software it is dealing with.
Code signing helps provide that identity.
A cryptographic signature allows the operating system to verify that application code comes from an expected signer and has not simply been modified arbitrarily.
Apple combines code signing with sandboxing and other runtime protections as part of its app-security model.
Android also signs application packages. Signatures can be used to establish trusted relationships between apps from the same developer and protect certain components or permissions.
This matters because some isolation decisions depend on identity.
For example, two applications signed by the same trusted developer may intentionally share certain resources, while an unrelated application should not receive that access.
Without dependable identity, access-control rules become much harder to enforce.
Read-Only System Components Protect the OS Itself
Separating applications from one another is useful, but the operating system also needs protection from those applications.
Apple states that the system partition on iOS, iPadOS, and visionOS is mounted read-only under normal circumstances. Third-party apps also do not receive APIs that simply let them escalate privileges and modify the OS or other apps.
Android uses different mechanisms, including verified partitions, SELinux policies, privilege separation, and Verified Boot.
The basic goal is the same.
Applications should not be able to rewrite core system components just because they found a bug in their own process.
This adds another containment boundary.
A compromised app first needs to escape its own sandbox. It then has to overcome system-level restrictions before it can modify something truly critical.
Layering these protections dramatically increases the amount of work required for a complete device takeover.
Hardware Security Protects the Most Valuable Secrets
Software isolation eventually reaches another boundary: hardware.
Modern smartphones increasingly place cryptographic keys, biometric operations, and other sensitive functions inside hardware-backed security environments.
Android devices may use a Trusted Execution Environment or StrongBox-backed key storage.
Apple devices use the Secure Enclave for highly sensitive security operations.
These systems are not simply another application sandbox. They create a stronger isolation boundary below the normal operating system.
Imagine malware manages to escape an app sandbox and obtain significant OS privileges.
That is already serious.
But if important private keys remain inside secure hardware and cannot be exported, the attacker still does not automatically gain every secret on the device.
This is why modern mobile security stretches from application-level isolation all the way down to silicon.
Each level protects something different.
Multiple Layers Reduce the Blast Radius of Vulnerabilities
No large operating system is completely free of bugs.
That reality is one of the strongest reasons for using several isolation mechanisms.
Imagine an attacker discovers a vulnerability inside a messaging application.
The first exploit compromises the app.
Sandboxing may keep the attacker inside its private environment.
A second exploit could theoretically escape that sandbox, but process policies and mandatory access controls provide more barriers.
Even if those are bypassed, secure boot, protected system components, and hardware-backed key storage may still limit what the attacker can do.
This is known as limiting the blast radius.
The goal is not to assume vulnerabilities will never exist. The goal is to make one vulnerability insufficient for complete compromise.
Sophisticated smartphone attacks therefore sometimes require exploit chains containing several different vulnerabilities.
That difficulty is a feature of layered security, not an accident.
Layered Isolation Also Improves Privacy
Isolation is not only about defending against hackers.
It also controls ordinary data collection.
A legitimate application may want access to more information than it actually needs.
Sandboxing, permissions, and platform-controlled services make unrestricted collection more difficult.
Apple’s security documentation explains that third-party apps must use explicitly provided system services when accessing information outside their own sandbox.
This creates opportunities for the operating system to require consent, provide limited data instead of full access, or deny the request entirely.
Modern photo permissions provide a useful example.
An application may be allowed to access only selected photos rather than receiving the user’s entire library.
The isolation boundary has not disappeared. The operating system has created a narrow, controlled window through it.
This is a much safer model than simply giving every app broad filesystem access.
Isolation Layers Still Need Updates
Multiple security layers do not eliminate the need for software updates.
Every layer can potentially contain implementation bugs.
The sandbox may have a vulnerability. The kernel may have another. A driver or trusted service may contain a seperate flaw.
Security patches close those gaps before they can easily become part of an exploit chain.
This is why long-term update support is increasingly important when evaluating smartphone security.
A device with strong hardware protections but years of unpatched software can gradually become much easier to attack.
Likewise, modern software cannot compensate indefinitely for obsolete security hardware.
Mobile security works best when hardware protections and continuously maintained software reinforce each other.
Mobile operating systems use multiple layers of app isolation because no single security mechanism is strong enough to handle every possible failure.
Sandboxing separates application data, process isolation protects memory, permissions restrict sensitive resources, SELinux and entitlements enforce additional policies, secure IPC controls communication, and code signing establishes software identity.
Hardware-backed security then creates another boundary for the most valuable secrets.
Together, these mechanisms follow a defense-in-depth strategy: if one protection fails, another should still limit the attacker’s reach.
When evaluating smartphone security, do not focus on one feature such as sandboxing or encryption. Look at the complete security architecture and update policy.
The safest mobile platform is one that assumes individual components may eventually fail – and is designed so that one failure does not become a failure of everything.
