
Smartphone security is often discussed as if it were mostly a software problem. People think about passwords, antivirus tools, permissions, operating-system updates, and suspicious apps.
But modern mobile security goes much deeper than that.
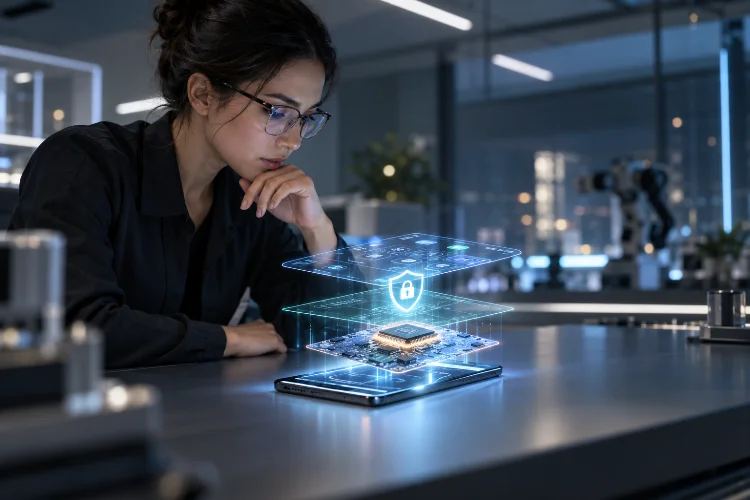
A secure smartphone depends on hardware and software working together from the moment the device starts. Hardware provides trusted foundations such as secure boot, cryptographic engines, protected key storage, and isolated execution environments.
Software builds on those foundations with sandboxing, app permissions, encryption policies, authentication systems, and regular security updates.
This is why mobile security depends on hardware and software integration rather than one layer alone.
Strong hardware without secure software can still be misused. Strong software running on weak hardware may lack a trustworthy way to protect keys or verify that the operating system has not been modified.
Modern platforms such as iOS and Android increasingly treat security as a full-stack problem. The safest design is not one giant defense, but many coordinated layers that reinforce one another.
Hardware Creates the Root of Trust
Security needs somewhere trustworthy to begin.
That starting point is often called a hardware root of trust.
A root of trust is a component that the system assumes cannot be modified easily. It may contain cryptographic keys, immutable boot code, or secure verification logic used to check the next stage of the startup process.
Android Verified Boot uses this concept directly. Google documents that the boot chain begins with a hardware-protected root of trust and then verifies the bootloader, kernel, and system partitions before execution continues.
Apple uses a similar model. Its hardware security architecture starts secure boot from immutable Boot ROM code built into the silicon, which then helps establish trust for later software stages.
Without this hardware foundation, software would have no strong way to know whether the code loading before it had already been tampered with.
Secure Boot Connects Hardware and Software
Secure boot is one of the clearest examples of hardware–software integration.
The hardware stores or protects trusted verification material. The software image carries cryptographic signatures. During startup, each stage checks the next before allowing it to run.
Android Verified Boot verifies executable code and system data before use, including critical partitions such as boot, system, and vendor. It also includes rollback protection to make it harder to reinstall an older, vulnerable operating-system version.
That means security does not begin after Android has already loaded.
It starts before the operating system is trusted.
Apple follows the same broader principle across its platforms, integrating silicon-level security with the startup process and software-update system.
Apple explicitly describes system security as building on unique hardware capabilities to protect boot, updates, and normal operating-system execution.
Hardware verifies software, while software depends on that hardware guarantee.
That relationship is fundamental.
Protected Hardware Keeps Keys Away From Normal Apps
Encryption is only useful if encryption keys remain protected.
If a smartphone stores sensitive keys as ordinary files accessible to the main operating system, a serious OS compromise could expose them.
Modern devices avoid that by using protected hardware environments.
Android provides hardware-backed Keystore support where key material can remain inside a Trusted Execution Environment or another secure environment rather than being directly exposed to apps.
Apple’s Secure Enclave performs a similar role. Apple describes it as a dedicated security subsystem isolated from the main application processor and designed to continue protecting sensitive data even if the main processor kernel is compromised.
The software can still request operations such as signing or decrypting.
But the key itself may never leave the protected hardware.
This distinction greatly improves security because malware has fewer opportunities to extract long-term secrets.
Software Sandboxing Controls What Apps Can Reach
Hardware isolation protects especially sensitive assets, but ordinary applications still need strong software boundaries.
That is where sandboxing becomes important.
Mobile operating systems limit what individual apps can access. An app usually cannot simply read another application’s files, inspect arbitrary memory, or access sensitive sensors without permission.
Android adds another software layer through SELinux, which enforces mandatory access controls even across highly privileged processes. Google includes SELinux as a core part of Android’s broader security architecture.
This works alongside hardware security rather than replacing it.
The secure hardware may protect a cryptographic key, while the operating system decides which app is allowed to request use of that key.
Similarly, biometric hardware may verify identity, while the software permission model determines what an authenticated app can actually do.
Security becomes stronger when each layer has a clearly defined job.
Trusted Execution Environments Bridge Both Worlds
A Trusted Execution Environment, or TEE, sits between conventional software and dedicated secure hardware.
A TEE is usually isolated from the main operating system using hardware controls.
Android’s Trusty TEE runs on the same processor as Android but is separated from the rest of the system through both hardware and software isolation. Google uses it for trusted services that should not run directly inside the normal Android environment.
This creates an important middle layer.
Not every security-sensitive task requires a completely separate physical chip, but many tasks still benefit from stronger isolation than a normal application process can provide.
The TEE can handle cryptographic services, trusted user-interface operations, key management, or other protected functions.
Software sends requests into that secure environment through controlled interfaces.
The hardware then enforces the isolation that keeps the trusted environment separate.
This is one reason mobile security cannot be cleanly divided into “hardware” and “software.” The strongest protections often exist precisely where the two meet.
Dedicated Security Chips Add Another Layer
Some smartphones go beyond a standard TEE and include dedicated security coprocessors.
Google’s Pixel devices are a good example.
Current Pixel hardware uses multiple layers that can include the Tensor security core, Titan M2 or newer Titan secure microcontrollers, and Trusty TEE. Google describes this as a multi-layer hardware security architecture.
Titan devices can provide hardware root-of-trust functions and dedicated cryptographic operations.
But even a dedicated chip still depends on software.
Firmware must be written securely. Cryptographic APIs need to be used correctly. The operating system must enforce proper access rules.
Google’s own secure-microcontroller guidance stresses that OEM engineers and developers must keep hardware protections enabled and perform cryptographic work through approved APIs.
That is the integration point again.
Secure hardware creates capability, but software determines whether that capability is used properly.
Biometrics Show Why Integration Matters
Face unlock and fingerprint authentication may look simple to users.
Behind the scenes, they rely on a chain of hardware and software components.
A sensor captures biometric information. Protected hardware processes or stores sensitive templates. The operating system handles policy and decides when authentication is required.
Apple’s Secure Enclave, for example, processes biometric data used by Face ID and Touch ID while keeping that information separated from normal operating-system access.
The software then uses the authentication result to unlock specific capabilities.
The app does not need direct access to the user’s fingerprint or face template.
This design is safer because the most sensitive information stays inside the protected hardware, while the software only receives a controlled result such as “authentication succeeded.”
Biometric security therefore depends on the entire path being trustworthy.
A secure sensor alone would not be enough.
Encryption Needs Hardware and Software Policies Together
Modern smartphones encrypt large amounts of user data.
Hardware can accelerate encryption and securely protect keys, but software decides when those keys become available.
For example, the operating system may tie certain encryption keys to the user’s passcode or biometric authentication.
It may also maintain different protection classes depending on whether the device is locked or unlocked.
Apple explicitly combines silicon-based security, cryptographic engines, Secure Enclave functions, and system-level data protection in its platform security architecture.
Android similarly combines hardware-backed Keystore, device encryption, verified boot, and OS-level access control.
This matters because encryption by itself is not enough.
A device can have strong cryptographic algorithms and still be insecure if software exposes decrypted data too freely or unlocks keys under weak conditions.
The algorithm, key storage, and access policy all need to work together.
Security Updates Are Still Essential
Hardware protections can make attacks much harder, but they do not remove the need for software updates.
Vulnerabilities can appear in kernels, drivers, system services, apps, or even secure firmware.
Regular updates close those weaknesses.
Apple’s security model explicitly includes secure and timely software updates as part of its broader platform design.
Google takes the same layered approach on Pixel, combining secure hardware with ongoing OS and security updates on supported models.
This shows why hardware should never be treated as a one-time solution.
A secure chip may protect keys for years, but the software around it continues evolving.
If the OS stops receiving patches, attackers may find new paths around otherwise strong hardware protections.
Long-term device security therefore depends partly on how long the manufacturer continues maintaining the software stack.
App Security Relies on Platform Security
Third-party developers also benefit from this integration.
A banking or messaging app does not need to build its own secure processor.
Instead, it can use platform APIs that connect software features to hardware-backed security.
Android apps can request keys from Android Keystore and, on compatible devices, those keys can be backed by secure hardware. The platform can also attest to properties such as verified boot state and whether the device was started from trusted software.
Developers can therefore build stronger authentication and encryption systems without directly controlling the security chip.
The same principle exists across Apple platforms through APIs for Keychain, Secure Enclave-backed keys, and biometric authentication.
The operating system becomes the bridge between app developers and the hardware security foundation.
That makes platform design incredibly important.
No Single Security Layer Is Enough
Mobile security is strongest when failures are contained.
If one app is compromised, sandboxing should limit access.
If the OS is attacked, protected hardware should still guard keys.
If someone tampers with system software, verified boot should detect the change.
If the device is stolen, encryption should make stored data difficult to read.
This is defense in depth.
The strategy assumes that no single layer is perfect.
Apple explicitly describes its devices as combining hardware, software, and services to work together for security. Android follows the same broad model through Verified Boot, hardware-backed Keystore, SELinux, Trusty TEE, encryption, and application isolation.
That integration is more resilient than relying on one impressive security feature.
A phone is secure because many protections overlap.
Mobile security depends on hardware and software integration because neither layer can provide complete protection alone.
Hardware creates trusted foundations through secure boot, protected key storage, TEEs, cryptographic engines, and dedicated security chips. Software builds on those foundations with sandboxing, permissions, encryption policies, authentication, updates, and app-level controls.
When these systems work together, attacks become much harder because compromising one layer does not automatically expose everything else.
For users, this means smartphone security should be evaluated as a complete platform. Look beyond marketing terms such as “secure chip” or “privacy protection.” Check how the device handles secure boot, hardware-backed keys, software isolation, patch support, and trusted execution.
The strongest mobile security is not one feature. It is a carefully integrated chain of defenses.
