
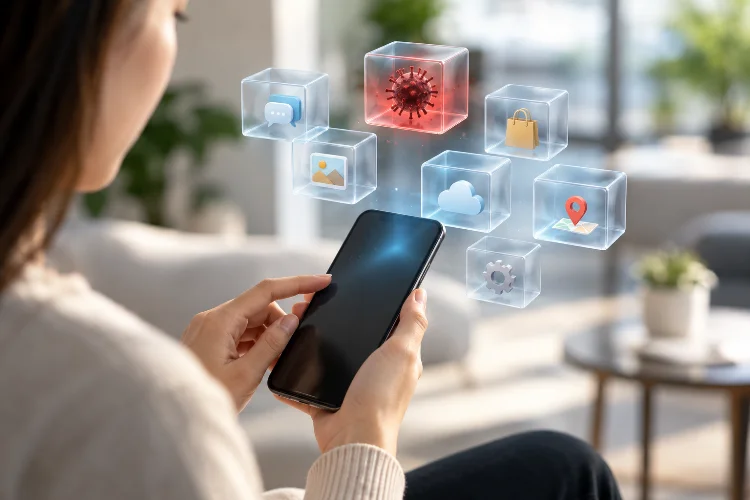
Smartphones run dozens or even hundreds of applications, and every one of them introduces some level of risk.
A messaging app handles private conversations, a banking app processes financial information, a photo editor accesses personal images, while games and social platforms often communicate continuously with remote servers.
What happens if one of those apps becomes compromised?
Ideally, the damage stays inside that application rather than spreading throughout the entire phone. This is the core idea behind application sandboxing on smartphones.
A sandbox creates boundaries around an app, limiting which files, processes, sensors, system resources, and other applications it can access. Android and iOS both rely heavily on this isolation model, although their implementations differ.
Sandboxing cannot guarantee that malicious software will never cause harm. What it does is dramatically reduce how much a compromised application can reach.
Instead of trusting every app to behave perfectly, the operating system assumes apps should only receive the access they actually need.
That simple principle has become one of the foundations of modern mobile security.
What Application Sandboxing Actually Means
Application sandboxing is essentially isolation enforced by the operating system.
Each app runs inside a restricted environment where its access to the rest of the device is limited.
On Android, the operating system assigns each application a unique user ID and normally runs it inside its own process. Linux-level permissions then help separate that application’s resources from those belonging to other apps.
Apple follows a similar principle.
On iPhone and iPad, third-party applications run inside sandboxes designed to prevent them from freely collecting or changing information belonging to other applications.
Each app receives its own container for files, while access to resources outside that container must go through system-controlled services.
Think of each app as living inside its own apartment.
The app can freely rearrange things inside its apartment, but it cannot simply walk into another apartment and inspect everything inside.
The operating system acts as the building security system controlling the doors.
Sandboxing Keeps App Files Separated
One of the most important jobs of a sandbox is protecting application data.
Consider a banking app storing account information and authentication-related data.
Without isolation, a random game installed on the same smartphone might theoretically attempt to browse through the bank app’s private files.
Sandboxing prevents that normal behavior.
Android gives apps dedicated private storage areas and uses its Linux-based security model to enforce separation. Android’s security architecture specifically includes per-app file-system isolation as one mechanism for protecting application resources.
Apple similarly gives third-party apps unique home directories. Other applications cannot simply inspect those directories unless the operating system provides an intentionally designed sharing mechanism.
This matters because apps inevitably store information locally.
Databases, cached messages, configuration files, authentication tokens, and downloaded documents may all exist somewhere on the device.
Sandboxing creates an important first barrier around that information.
Process Isolation Limits the Spread of Exploits
Separating files is useful, but apps also need process isolation.
Each running application occupies memory while executing its code.
If apps shared unrestricted access to process memory, one malicious application could potentially inspect another app’s passwords, messages, or temporary data while that information was being processed.
Modern operating systems prevent this through process boundaries and memory protections.
Android builds its application sandbox on Linux user and process isolation. Even native code normally remains constrained by the same sandbox environment.
Google’s documentation specifically notes that this architecture is designed to stop a rogue application from harming other apps or the wider system.
That containment becomes especially valuable when an application contains a vulnerability.
Suppose an attacker exploits a bug in a photo-editing app.
Without sandboxing, controlling that application might immediately provide access to the entire device.
With strong isolation, the attacker still has to escape the sandbox before reaching more sensitive system resources.
That additional step significantly raises the difficulty of an attack.
Permissions Create Controlled Openings in the Sandbox
A completely isolated app would not be very useful.
Navigation software needs location data. Camera apps need camera access. Messaging platforms may require a microphone, contacts, or photos.
Mobile operating systems therefore create controlled openings through permission systems.
Android protects sensitive APIs and resources with permissions. Applications must declare or request access to capabilities such as cameras, location, or other protected functions rather than receiving unrestricted access automatically.
Apple also carefully mediates application access to user information as part of its broader app security model.
Permissions and sandboxing work together.
The sandbox begins with limited access, while permissions selectively expand what an application can do.
This is much safer than giving every installed app access to every sensor and data source by default.
It also gives users some control over their personal information.
A weather app may genuinely need location access, but there is little reason for a simple calculator to read your photographs.
Apps Can Still Communicate Through Controlled Channels
Modern applications sometimes need to interact with each other.
For example, a photo application may share an image with a messaging platform. A password manager may provide credentials to another app. A payment service may return an authorization result.
Sandboxing does not prevent all communication.
Instead, operating systems provide controlled mechanisms for inter-process communication.
Android includes secure IPC mechanisms that allow applications in different processes to exchange information while maintaining process boundaries. App signing and permission rules can further restrict which applications are allowed to access particular components.
This is an important design principle.
Instead of allowing one app to reach directly into another app’s memory or private files, information moves through explicitly defined interfaces.
That makes communication easier to monitor and restrict.
Well-designed apps expose only the capabilities they actually want other applications to use.
Android Uses SELinux to Strengthen Isolation
Android’s sandbox has evolved substantially over time.
Basic application isolation originally depended heavily on Linux user IDs and discretionary access controls.
Later versions added stronger SELinux protections.
SELinux provides mandatory access control rules defining which processes can interact with particular resources.
Android 9, for example, required non-privileged apps targeting the appropriate API level to run in individual SELinux sandboxes, providing another layer of per-app isolation.
Android also introduced seccomp-bpf filters for applications, limiting the system calls available to app processes and strengthening the boundary between apps and the kernel.
These protections demonstrate an important security concept: isolation should not rely on only one mechanism.
Unique user IDs provide one boundary.
SELinux adds another.
System-call filtering adds another.
If an attacker manages to bypass one restriction, another may still limit what the compromised process can accomplish.
Apple Combines Sandboxing With Code Signing
Apple’s mobile security model also combines multiple protections.
On iPhone and iPad, strict sandboxing works alongside centralized application distribution and code signing. Apple describes these three mechanisms as central principles of its app-security architecture.
Code signing helps the operating system verify who signed an application and whether executable code has been modified unexpectedly.
Sandboxing then controls what that application can do after it begins running.
Apple also mounts the operating-system partition as read-only under normal conditions and does not expose APIs allowing ordinary apps to simply increase their privileges and modify other applications or the operating system.
This layered design reduces the chance that one malicious or compromised app can change the entire platform.
Again, the key concept is containment.
Security assumes individual applications might eventually contain bugs. The system therefore limits the damage those bugs can cause.
Sandboxing Makes Malware Less Powerful
Imagine downloading a malicious wallpaper application.
Without strong isolation, that app could potentially search the device for browser cookies, banking databases, private documents, messages, and authentication tokens.
Sandboxing blocks much of that direct access.
The malicious program remains constrained by its application identity and granted permissions.
This does not mean malware becomes harmless.
If users grant excessive permissions, malicious software might still abuse camera, microphone, location, contacts, accessibility features, or other legitimate capabilities.
A sandbox escape vulnerability can also allow attackers to bypass isolation.
But forcing attackers to defeat multiple protections is enormously valuable.
Security is often about reducing the attacker’s available options.
A malicious app trapped inside a tightly restricted sandbox is considerably less dangerous than one that automatically receives system-wide access.
Sandboxing Helps Protect System Stability Too
Security is not the only benefit.
Isolation also improves reliability.
A badly written application may leak memory, crash repeatedly, or behave unpredictably. Process separation reduces the chance that these failures directly corrupt unrelated applications.
If one social-media app crashes, your banking application should continue operating.
The operating system can terminate the failing process without necessarily affecting others.
Android’s Linux-based architecture specifically uses user and process isolation not only to protect data but also to prevent one application from consuming or interfering with another application’s resources improperly.
This separation makes smartphones remarkably resilient considering how much third-party software users install.
Hundreds of applications from different developers can coexist on one device without being fully trusted by one another.
The sandbox makes that ecosystem practical.
Sandboxes Still Need Secure App Design
Sandboxing is powerful, but developers cannot treat it as a replacement for secure coding.
An application can still expose its own data accidentally.
For example, a developer might create an exported Android component without appropriate permission controls or store sensitive information somewhere intentionally shared with other applications.
Apps can also communicate with remote servers insecurely.
A sandbox cannot protect data after an app deliberately sends it across an unencrypted or compromised network connection.
Developers therefore need to understand the boundaries they expose.
Sensitive components should remain private unless sharing is necessary. Authentication tokens should be stored appropriately, permissions should be minimized, and external inputs should always be treated carefully.
The sandbox provides a strong baseline.
Application developers still determine how securely their own code behaves inside and around that boundary.
Sandboxing Cannot Stop Every Attack
No sandbox is impossible to escape.
Operating systems, kernels, drivers, and hardware can contain vulnerabilities.
Attackers sometimes combine multiple exploits in a chain.
The first bug may compromise an application. A second vulnerability escapes the sandbox. Another exploit might elevate privileges or attack the kernel.
That is why smartphone security uses defense in depth.
Apple combines app sandboxing with code signing, system security, hardware protections, encryption, and controlled access to user information.
Android similarly combines the Application Sandbox with SELinux, secure IPC, app signing, permissions, verified boot, encryption, and hardware security mechanisms.
The sandbox is one barrier in a larger security system.
Its real strength is making successful attacks require additional vulnerabilities instead of giving compromised software an easy path to everything else.
Application sandboxing reduces smartphone security risks by assuming that apps should never automatically trust one another.
Android isolates applications through unique identities, separate processes, file permissions, SELinux policies, and controlled IPC.
Apple similarly gives third-party apps isolated containers and combines sandboxing with code signing and carefully mediated access to system resources.
These boundaries cannot prevent every vulnerability, but they greatly reduce the blast radius when something goes wrong.
For users, the practical lesson is simple: keep your operating system updated and think carefully before granting powerful permissions. For developers, minimize exposed components and request only the access your app genuinely needs.
A secure smartphone does not assume every application is safe. It is designed so that even an unsafe application has very little room to move.
